procurement privacy considerations
Strong procurement privacy considerations begin before a solicitation is published. A procurement file may contain supplier contact details, pricing, contracts, evaluation notes, employee information and operational records. The team must decide what information is needed, who may access it, how it will be protected, and when it may be deleted or retained.
Key Takeaways
- Privacy planning belongs at the start of the procurement cycle, since waiting until a contract is signed leaves little room to control how sensitive records are collected and shared.
- A single procurement file can hold many kinds of personal and business information, so identifying each record type early helps teams apply the right safeguards to each one.
- Clear decisions about who can view, edit and store procurement records reduce the risk of accidental disclosure during evaluation and contract administration.
- Retention and deletion rules are just as important as protection measures, because keeping records longer than needed creates ongoing privacy exposure.
- Reviewing how vendors handle personal information before award gives public-sector teams a practical way to manage third-party privacy risk.
This guide offers a practical Canadian public-sector starting point. It is educational guidance, not legal advice. Each organization should confirm requirements with its privacy officer, access-to-information lead, records manager and legal counsel. Teams may also consider Procurement Training for Teams, which provides a Canadian-focused public sector procurement curriculum.
Assess privacy during planning, not after supplier selection. Map the information, identify the purpose, limit collection, define access controls, ask suppliers how they handle it, and place clear obligations in the solicitation and contract. Review controls during delivery, changes, renewal and closeout.
Understanding Procurement Privacy Considerations in Canada
What Are Procurement Privacy Considerations?
These are the decisions and controls used to manage personal information and other sensitive procurement records throughout purchasing. Personal information can include names, business contact details tied to an identifiable person, signatures, financial information, user credentials or evaluation comments. Scope depends on the service, information collected and public body involved.
Ask what information is involved, why it is needed, where it will go, and who is responsible. Record the answers in the procurement plan, requirements, evaluation materials, contract and closeout record. A privacy review may be appropriate when a service collects, uses, discloses or stores personal information for the organization.
Why They Matter in Canadian Public-Sector Procurement
Public procurement must produce a defensible decision while protecting people and public trust. Weak handling can expose bid details, create unnecessary access, complicate an access-to-information request or leave uncertainty about supplier practices. Early review allows time to revise requirements, obtain advice and address gaps before award. Treasury Board of Canada Secretariat guidance supports considering privacy before contracting decisions.
Privacy is also a governance issue. The file should show the collection purpose, authority, access parties, safeguards and decisions made when risk was identified. Clear ownership helps procurement, program, information technology, security and privacy staff work from one record.
Privacy, Confidentiality, Cybersecurity, Access to Information and Records Management
These subjects connect but are not interchangeable. Privacy concerns fair and lawful handling of personal information. Confidentiality limits disclosure of information that should not be shared. Cybersecurity protects systems and data from unauthorized access, alteration, loss or disruption. Access to information governs requests and disclosure, subject to applicable exemptions. Records management covers classification, retention, disposition and retrieval.
| Area | Practical procurement question | Evidence to retain |
|---|---|---|
| Privacy | Is the collection and use of personal information necessary and authorized? | Privacy advice, information map and documented purpose |
| Confidentiality | Which bid, contract or operational details require restricted access? | Confidentiality terms and access list |
| Cybersecurity | What safeguards protect systems, accounts, transfers and stored data? | Security requirements and review results |
| Access to information | Could the record be requested, and which exemptions may apply? | Organized procurement file and disclosure review |
| Records management | How long must records be kept, and how will authorized disposition occur? | Retention classification and disposal confirmation |
Key Canadian Legislation and Frameworks
Requirements vary by jurisdiction and organization. Federally, the Privacy Act applies to personal information held by federal government institutions, while the Personal Information Protection and Electronic Documents Act may apply in specified private-sector contexts. Provinces and territories may have public-sector privacy statutes, access-to-information laws, health-information rules and procurement policies with different scopes. Municipal organizations may be subject to provincial rather than federal public-sector rules.
Use official guidance from the responsible government, including Treasury Board of Canada Secretariat privacy material and the applicable provincial or territorial privacy commissioner. Before finalizing a solicitation or contract, confirm with the privacy officer or legal counsel the governing statute, cross-border rules, breach processes, records obligations and any need for a privacy impact assessment.
Privacy Across the Procurement Lifecycle: From Planning to Closeout
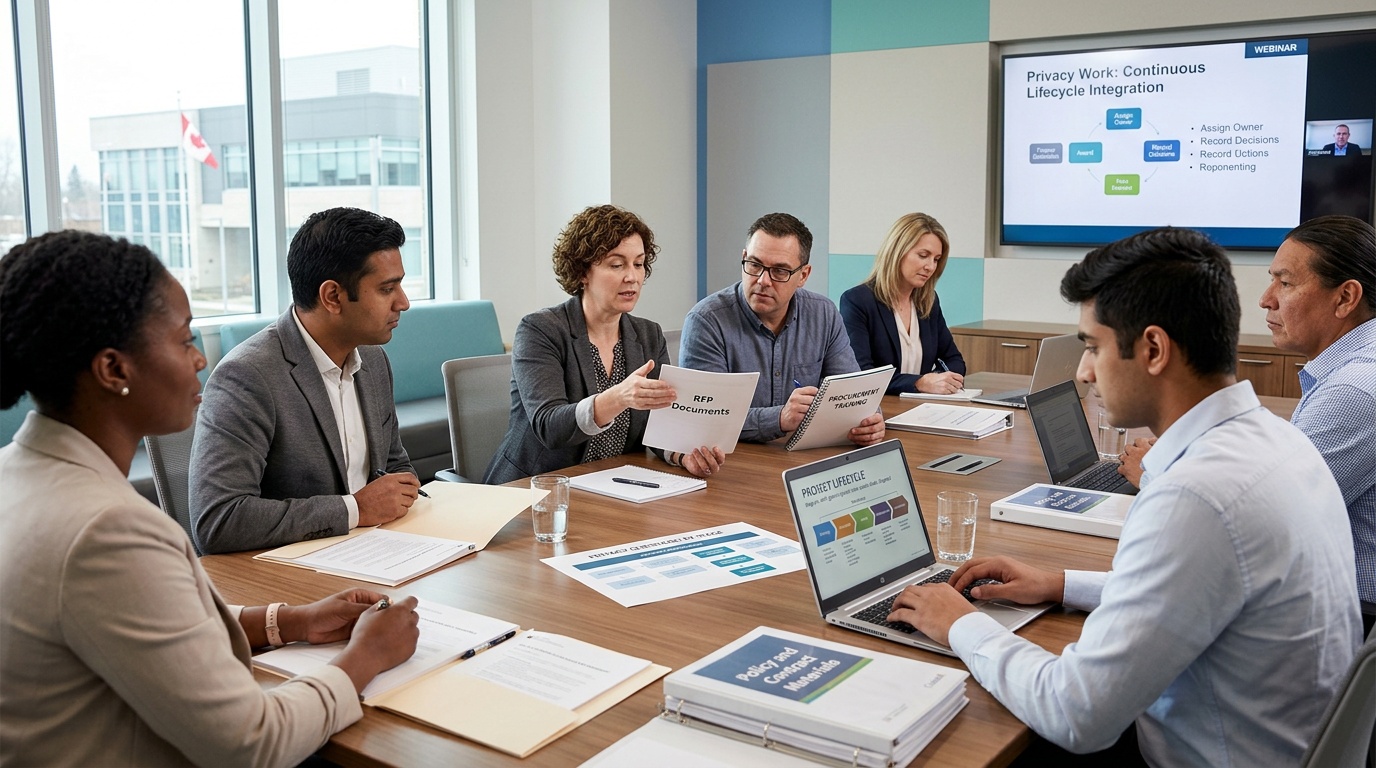
Privacy work is not a single approval gate. It follows the lifecycle, with different questions at each stage. Assign an owner, record the decision and reassess when scope, technology, supplier access or data use changes.
Stage 1: Planning and Strategy, Embedding Privacy Early
Begin with the business need and describe the service without collecting more personal information than required. Identify employee records, resident information, payment details, video, location data, health information, identity documents or supplier personnel records involved. Map information from collection through transfer, storage, access, backup, return and destruction.
Identify the program owner, data owner, privacy contact, security contact and contract manager. Ask whether a privacy impact assessment, threat assessment or records consultation is needed, especially when a service processes information for the organization, connects to a public system or introduces automated decision support.
Stage 2: Specification and Solicitation, Defining Requirements
Translate the assessment into measurable requirements covering permitted purposes, user roles, authentication, encryption, incident notification, audit support, subcontractors, data location, retention, return and secure deletion. Distinguish mandatory requirements from rated features so evaluators apply them consistently.
Tell bidders how confidential information will be handled and which records may be subject to access-to-information obligations. Avoid unnecessary personal information in bids. Provide a secure submission route and define access to bids, evaluation notes and clarification correspondence.
Stage 3: Evaluation and Selection, Vendor Due Diligence
Evaluate privacy and security responses against published criteria. Seek details about data flows, hosting, subcontractors, access controls, incident response, training and deletion. A general certification or policy statement is not proof that the service meets specific needs.
Allow time for privacy and security review, clarification and correction before award. Record questions, answers, conditions and unresolved risks. Refer material post-evaluation changes in data handling back to reviewers.
Stage 4: Award and Contract Management, Ongoing Oversight
The contract should make the approved approach enforceable. Include purpose, permitted data elements, access restrictions, confidentiality, safeguards, incident escalation, audit cooperation, subcontracting approval, data location, retention, return and disposal, plus a process for changes, renewals, service credits or remedies where appropriate.
Confirm that practice matches the contract by reviewing access lists, accounts, data extracts, service reports, incidents, subcontractor changes and renewal documents. The contract manager should know notification, change-approval and information-flow pause responsibilities.
Stage 5: Closeout, Data Disposition and Record Keeping
Closeout includes reconciling accounts, copies, exports, backups and shared folders. Obtain return or destruction confirmation, subject to legal holds, retention schedules and public-record obligations, and confirm subcontractor compliance.
Retain requirements, evaluation records, contract, privacy review, change approvals, monitoring notes and closeout confirmation under the organization’s records classification and retention authority. Do not delete procurement records merely because the service ended.
A Practical Decision Path
Use this path before issuing a solicitation or approving a material contract change:
- Does the work involve personal information or sensitive procurement records? If no, document the basis and continue. If yes, continue.
- Will a supplier collect, use, disclose, host or access the information? If yes, involve privacy and security contacts before finalizing requirements.
- Does the activity introduce new technology, extensive monitoring, sensitive information, public-facing services or automated analysis? If yes, ask whether a privacy impact assessment or added risk review is required.
- Are controls, contract terms and operational owners clear? If no, resolve the gap before award or document an authorized exception.
- Has the service, data use or supplier chain changed? If yes, reassess rather than relying on the original approval.
Teams seeking a shared foundation can use Procurement Training for Teams to build consistent public-sector knowledge across procurement, program, contract-management and operational staff. A common vocabulary helps identify privacy questions early and preserve an evidence trail.
Vendor Risk Management and Due Diligence: A Privacy Checklist
Vendor review should test how a supplier will handle information in the proposed service, not merely whether it has a general privacy policy. Effective procurement privacy considerations connect practices to the data, systems, users, subcontractors and contract duties involved. Assign a coordinator and involve the program owner, privacy officer, security specialist and contract manager when warranted.
Assessing Supplier Data Handling Practices
Ask for the complete information flow: collection, input, access, use, disclosure, transfer, hosting, backup, retention and deletion. Identify supplier personnel access, support locations, and copies in testing, analytics or service-improvement environments.
Review role-based access, authentication, encryption, logging, incident response, training, secure development and change management against information sensitivity. Record assumptions, gaps, conditions and follow-up owners.
Key Questions for Vendor Privacy Questionnaires
A questionnaire should produce evidence rather than broad assurances. Ask:
Require suppliers to distinguish current from planned controls, with an owner and completion date for each remedy. Evaluate responses against solicitation requirements and document clarifications and exceptions before award.
Understanding Subprocessors and Data Flows
Suppliers may rely on cloud hosts, payment providers, support centres, analytics services or other subprocessors. Request each party’s function, access level, processing location and authorization process. Require notice of material changes and define review, approval, objection or termination rights where appropriate.
Draw a flow diagram showing movement between the organization, supplier, subprocessors and end users. It can expose copies, international transfers, shared environments or support access. Revisit it when the service changes, not only at renewal.
Evidence of Compliance: What to Ask For and Review
Request service-specific policies, independent assurance reports, penetration-test summaries, incident procedures, training records, access-review evidence and deletion statements. Review scope, dates, exclusions and corrective actions. Keep a record linking each requirement to the response, reviewer, clarification and outcome.
Special Considerations for AI and Emerging Technologies
AI procurement requires questions about inputs, outputs, prompts, training, testing, human review, monitoring and model updates. Confirm whether bid materials, confidential records or personal information will train a model or improve a shared service. Unless approved, prohibit those uses and restrict prompt and output retention.
Ask how the supplier addresses inaccurate or discriminatory outputs, unauthorized disclosure, prompt injection, access logging and explainability. Define approval boundaries for automated recommendations and require human oversight for decisions affecting people. Teams can use Procurement Training for Teams, which includes a Canadian-focused public sector procurement curriculum. Procurement Training for Teams also supports a shared review practice through its progressive certification pathway from essentials to procurement expert level.
Operationalizing Privacy: Practical Tools and Accountability
Strong procurement privacy considerations become useful when assigned to people, recorded in the file and checked during delivery. Practitioners need a method for deciding what to collect, who may access it, which approvals are required and what evidence remains.
A Canadian Public-Sector Privacy Considerations Checklist
Use this checklist during planning, before award, for contract changes and at closeout. Adapt it to the organization’s privacy statute, records schedule, security standard and approval process. Assign an owner and review date.
Worked Example: Procuring a Municipal IT Service
Imagine a municipality procuring a service desk platform containing employee names, work contact details, service requests, device identifiers and technical-problem notes. The team confirms each data element’s purpose and removes unnecessary fields. The program owner identifies the information owner, while privacy and security staff review hosting, support access, authentication, audit logs and incident reporting.
The solicitation asks suppliers where information will be stored, which subprocessors may access it, how accounts will be removed and how records will be returned. Evaluators link responses to requirements. Before award, the team records conditions such as subcontractor approval or completion of a security action. During delivery, the contract manager reviews access reports and changes. At closeout, the municipality confirms account removal and authorized disposition while retaining records under its schedule.
Escalation Triggers: When to Involve Privacy, Legal and Security Teams
Escalate when a supplier handles personal information, sensitive operational data, health information, identity documents or large data sets. Referral is also appropriate for international hosting, new monitoring, automated decision support, biometric functions, public-facing services, material subcontractor access, suspected incidents or unclear ownership. Legal review may address jurisdiction, statutory authority, remedies, disclosure duties and records obligations.
Provide specialists with the business purpose, information map, requirements, supplier questions and timeline. Procurement coordinates the process; specialist reviewers advise within their mandates. The file should show advice received and how it was addressed.
Building Evidence for Procurement Decisions
Retain the approved need, data inventory, privacy and security reviews, solicitation clauses, evaluation notes, clarification record, conflict declarations, approvals, contract, change decisions and monitoring reports. Keep evidence proportionate: a reviewer needs the decision, rationale, owner, date and supporting document.
Use a requirements matrix linking each privacy requirement with the supplier response, evaluator, result and follow-up action. Restrict personal information in evaluation notes, use consistent file naming and record approval sources.
Segregation of Duties and Operational Controls
Separate responsibilities where one person could create, approve, receive and pay for the same transaction. For technology, the requester should not approve their own access, and an account administrator should not independently approve access reviews. For goods, receiving staff should confirm delivery while another authorized role approves payment.
Use access lists, approval workflows, periodic reviews, exception logs and reconciliation reports. For teams developing shared capability, Procurement Training for Teams provides a Canadian-focused public sector procurement curriculum. Procurement Training for Teams also includes a progressive certification pathway from essentials to procurement expert level.
Frequently Asked Questions
What are the 5 P's in procurement?
The 5 P’s in procurement are preparation, purpose, process, people and performance. Procurement privacy considerations fit each area by defining the need, limiting personal information collection, assigning responsibilities, setting fair procedures and checking supplier compliance. Canadian public-sector teams should document privacy decisions from planning through contract closeout.
What are the 7 principles of procurement?
The 7 principles of procurement are value for money, fairness, transparency, competition, accountability, integrity and sustainability. Procurement privacy considerations support these principles by protecting personal information, restricting access to evaluation records and keeping a clear decision record. Organizations should confirm the applicable requirements with their privacy and legal advisors.
What are the 5 R's of procurement?
The 5 R’s of procurement are the right quality, quantity, time, price and source. Procurement privacy considerations add another practical check: collect the right information for a defined purpose, from an appropriate source, and retain it only as long as authorized. This approach helps prevent unnecessary data collection and access.
What are the 5 pillars of procurement?
The 5 pillars of procurement are value, process, people, technology and governance. Procurement privacy considerations apply across all five by setting information requirements, training staff, protecting systems, assigning ownership and recording decisions. A Canadian public-sector team should review privacy controls when requirements, suppliers, technology or data use change.
What are the 7 R's of procurement?
The 7 R’s of procurement commonly refer to the right product, quantity, condition, place, time, customer and cost. Procurement privacy considerations extend this checklist to personal information by asking what data is needed, where it will be stored, who may access it and when it must be returned or deleted.
How do procurement principles protect supplier and employee information?
Procurement principles protect supplier and employee information through purpose limitation, controlled access, secure handling, transparency and accountable records. Procurement privacy considerations should cover contact details, pricing, signatures, evaluation comments and credentials. Solicitation documents and contracts should state supplier obligations for collection, use, storage, disclosure, breach response and disposition.
Which procurement framework is best for managing privacy in Canada?
No single procurement framework applies to every Canadian organization, so the best approach combines procurement principles with the applicable privacy, access-to-information, security and records rules. Federal, provincial, territorial and municipal requirements may differ. A privacy officer, access-to-information lead, records manager and legal counsel can confirm the correct framework.